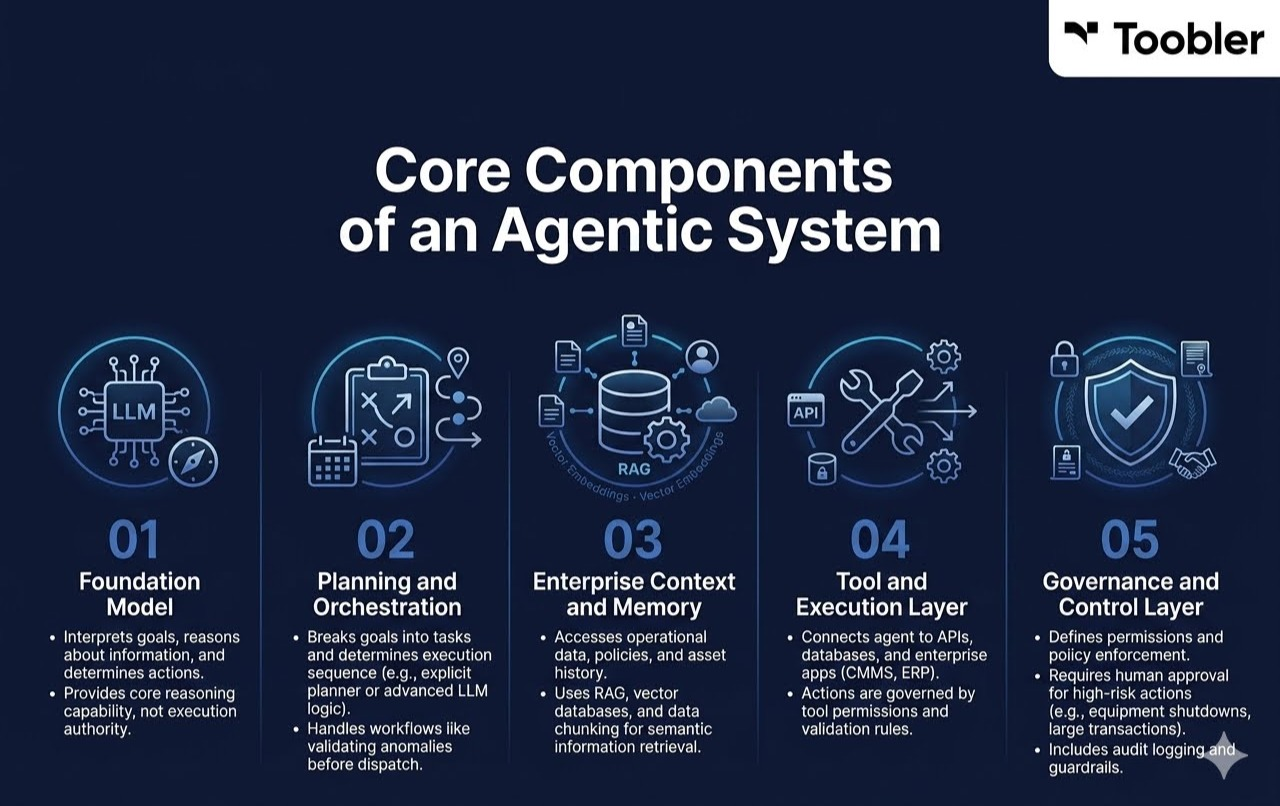
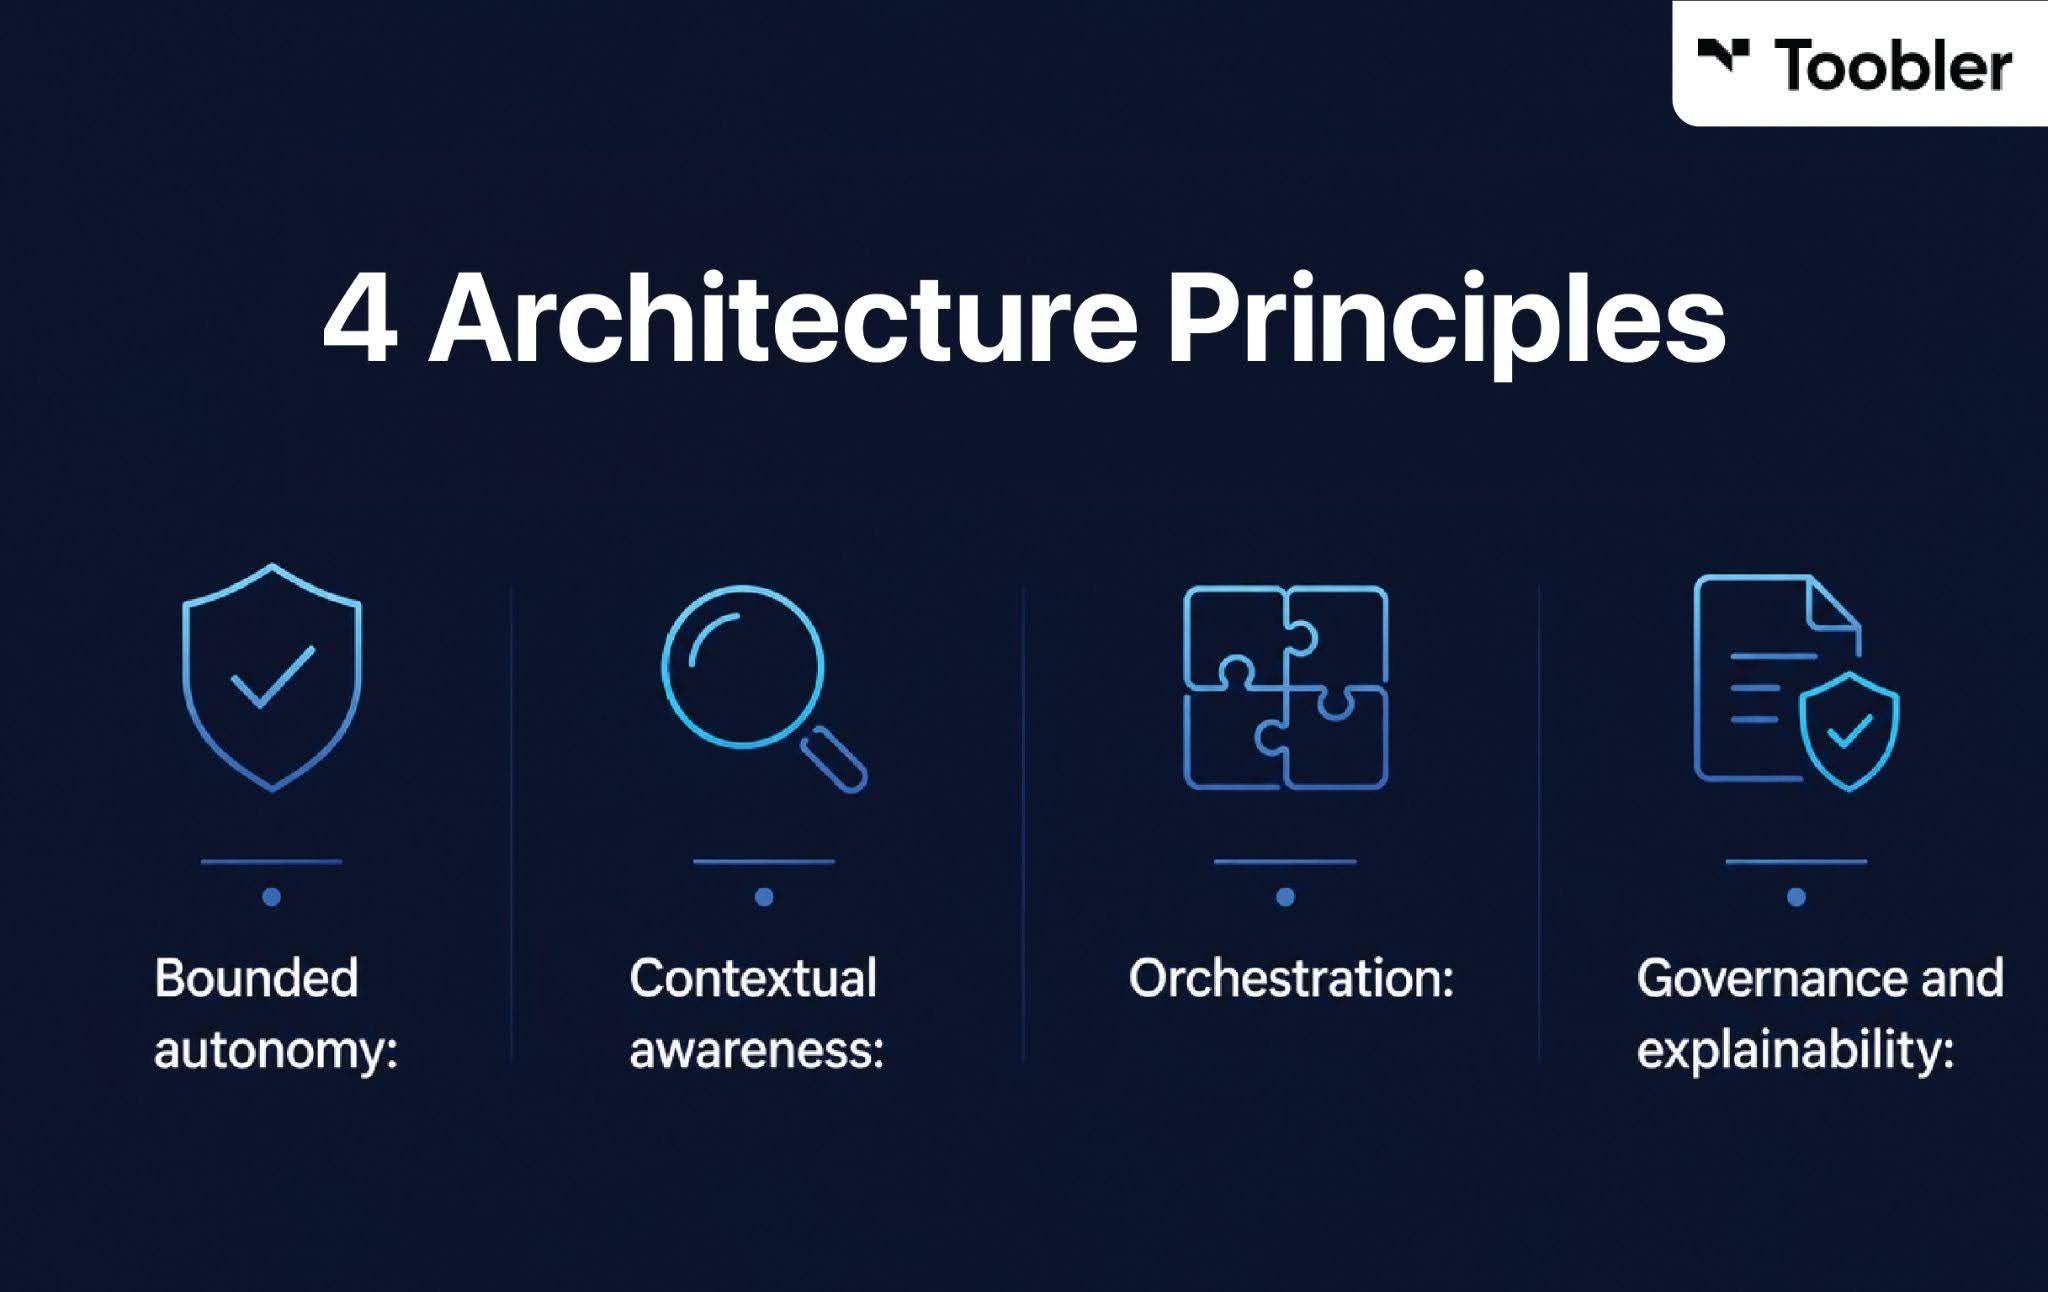
Governance becomes more important as an agent moves from providing recommendations to taking actions on behalf of employees or enterprise systems. The appropriate controls should therefore depend on the agent's level of autonomy, the systems it can access, the actions it can perform, and the potential impact of failure.
For industrial enterprises, governance should be designed into the architecture rather than added after deployment
Risk-Based Autonomy
Not every agent requires the same level of control. A practical approach is to classify actions according to their risk and define the corresponding level of autonomy.
Low-risk actions: Agents can perform predefined actions automatically within approved permissions.
Medium-risk actions: Agents can prepare or initiate an action but notify an authorised user or require additional validation.
High-risk actions: Actions involving safety, critical equipment, significant financial exposure, or other material consequences require explicit human approval.
For example, an agent may automatically retrieve equipment history and prepare a maintenance recommendation. Creating a work-order request may be permitted automatically, while shutting down production equipment would require an authorised human decision.
This approach prevents enterprises from applying the same governance model to every agent and allows autonomy to increase only where the risk is understood and controlled.
Human Oversight
Enterprises must define human-in-the-loop controls before deploying an agent. The system should specify:
which actions require approval;
who is authorised to approve them;
what information the reviewer receives;
when the workflow must be escalated;
and what happens if approval is unavailable or an action fails.
Human oversight should be targeted at decisions where human judgment, accountability, or safety is required rather than forcing users to manually approve every low-risk action.
Identity, Access, and Tool Permissions
Agents should operate with controlled identities and permissions rather than broad access to enterprise systems.
Access should be limited according to the agent's role and the tools it needs to perform its assigned workflow. Security and IAM teams must manage credentials and secrets through appropriate enterprise security mechanisms, ensuring they never expose them in prompts or agent context.
Tool-level permissions should also distinguish between actions such as:
Read data → Prepare action → Request approval → Execute action
This separation reduces the risk that an agent can move directly from reading information to performing a high-impact operation.
OT/IT Security Boundary
Industrial deployments require particular attention to the boundary between enterprise IT and operational technology.
Network segmentation and existing industrial cybersecurity controls must protect systems like SCADA, DCS, and PLC-connected environments.
IEC 62443 can provide a relevant framework for designing and managing industrial automation and control-system cybersecurity.
Data Governance
Agentic systems may process operational telemetry, enterprise transactions, maintenance records, employee information, and other sensitive data. Enterprises should therefore define:
Security architects must tailor these controls to the specific data types and systems involved, rather than applying a single, blanket policy to every data source.
Auditability and Observability
Enterprise agents should maintain an auditable record of significant activity. This can include:
the user, system, or event that initiated the workflow;
relevant inputs and retrieved data;
policies applied;
tools invoked;
actions requested or executed;
human approvals;
outputs and outcomes;
failures and exceptions;
timestamps and system identifiers.
This provides organisations with a traceable record of what the agent did, what information and policies were involved, what tools it used, and who approved consequential actions.
Logging by itself does not make an AI system compliant. Audit records are one component of a broader governance framework that also includes access control, policies, security, testing, human oversight, and operational monitoring.
Evaluation and Continuous Monitoring
Governance does not end when an agent is deployed. Enterprises should continuously evaluate whether agents are operating within their intended boundaries.
Monitoring can include:
task success and failure rates;
incorrect or rejected tool calls;
escalation frequency;
policy violations;
latency and availability;
cost and resource usage;
and changes in performance over time.
Agents should also have defined fallback and escalation mechanisms when data is unavailable, a tool fails, or the agent cannot confidently complete the requested workflow.
The objective is not to make every agent fully autonomous. It is to establish the appropriate level of autonomy for each workflow and surround that autonomy with controls proportionate to the risk.